ATF responds to 'major' cybersecurity incident after ransomware gang's claims
The Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) confirmed it is investigating a significant cybersecurity breach after the Qilin ransomware group listed the U.S. federal law enforcement agency on its data leak site.
In a statement on its website, the ATF said the incident involved a standalone computer system containing information about targets of ATF investigations. The agency emphasized that the compromised system was not connected to its broader enterprise network, eForms system, or any other internal systems. As a result, the ATF stated that there is no evidence the breach has impacted its operations.
An ATF spokesperson told a news outlet that the agency is coordinating with the U.S. Department of Justice (DOJ) to investigate the incident, which has been classified as a “major incident” under federal guidelines. The ATF added that it took immediate action to block connections to the affected environment upon discovering the breach. However, the spokesperson declined to provide further details, citing the ongoing investigation.
The Qilin ransomware group, which has been linked to Russia, added the ATF to its leak site shortly before the agency posted its public statement. The ransomware gang has been notably active in 2024, including a high-profile attack on Synnovis, a pathology provider in the UK, which disrupted National Health Service (NHS) services. Comparitech, a cybersecurity research firm, reported that Qilin was responsible for 125 out of 799 ransomware incidents recorded in July, making it one of the most active groups that month.
The ATF’s response follows growing concerns about cyber threats targeting U.S. government agencies. While the agency has not disclosed whether any data was stolen or if a ransom demand was made, the incident underscores the persistent risks posed by ransomware gangs to critical institutions.
Federal guidelines classify major cybersecurity incidents as those that could cause significant harm to national security, public health, or safety. The ATF’s designation as a major incident suggests the breach is being treated with high priority within the U.S. government’s cybersecurity framework.
#Cybersecurity #Ransomware #ATF #Qilin #DOJ #Cyberattack #DataBreach
Comments (0)
No comments yet — be the first to weigh in.
Energy biz SSE smacked around in court by a guy and AI
An Oxford doctoral student has defeated British energy provider SSE Energy Supply in court after utilizing artificial intelligence models to build his legal def...
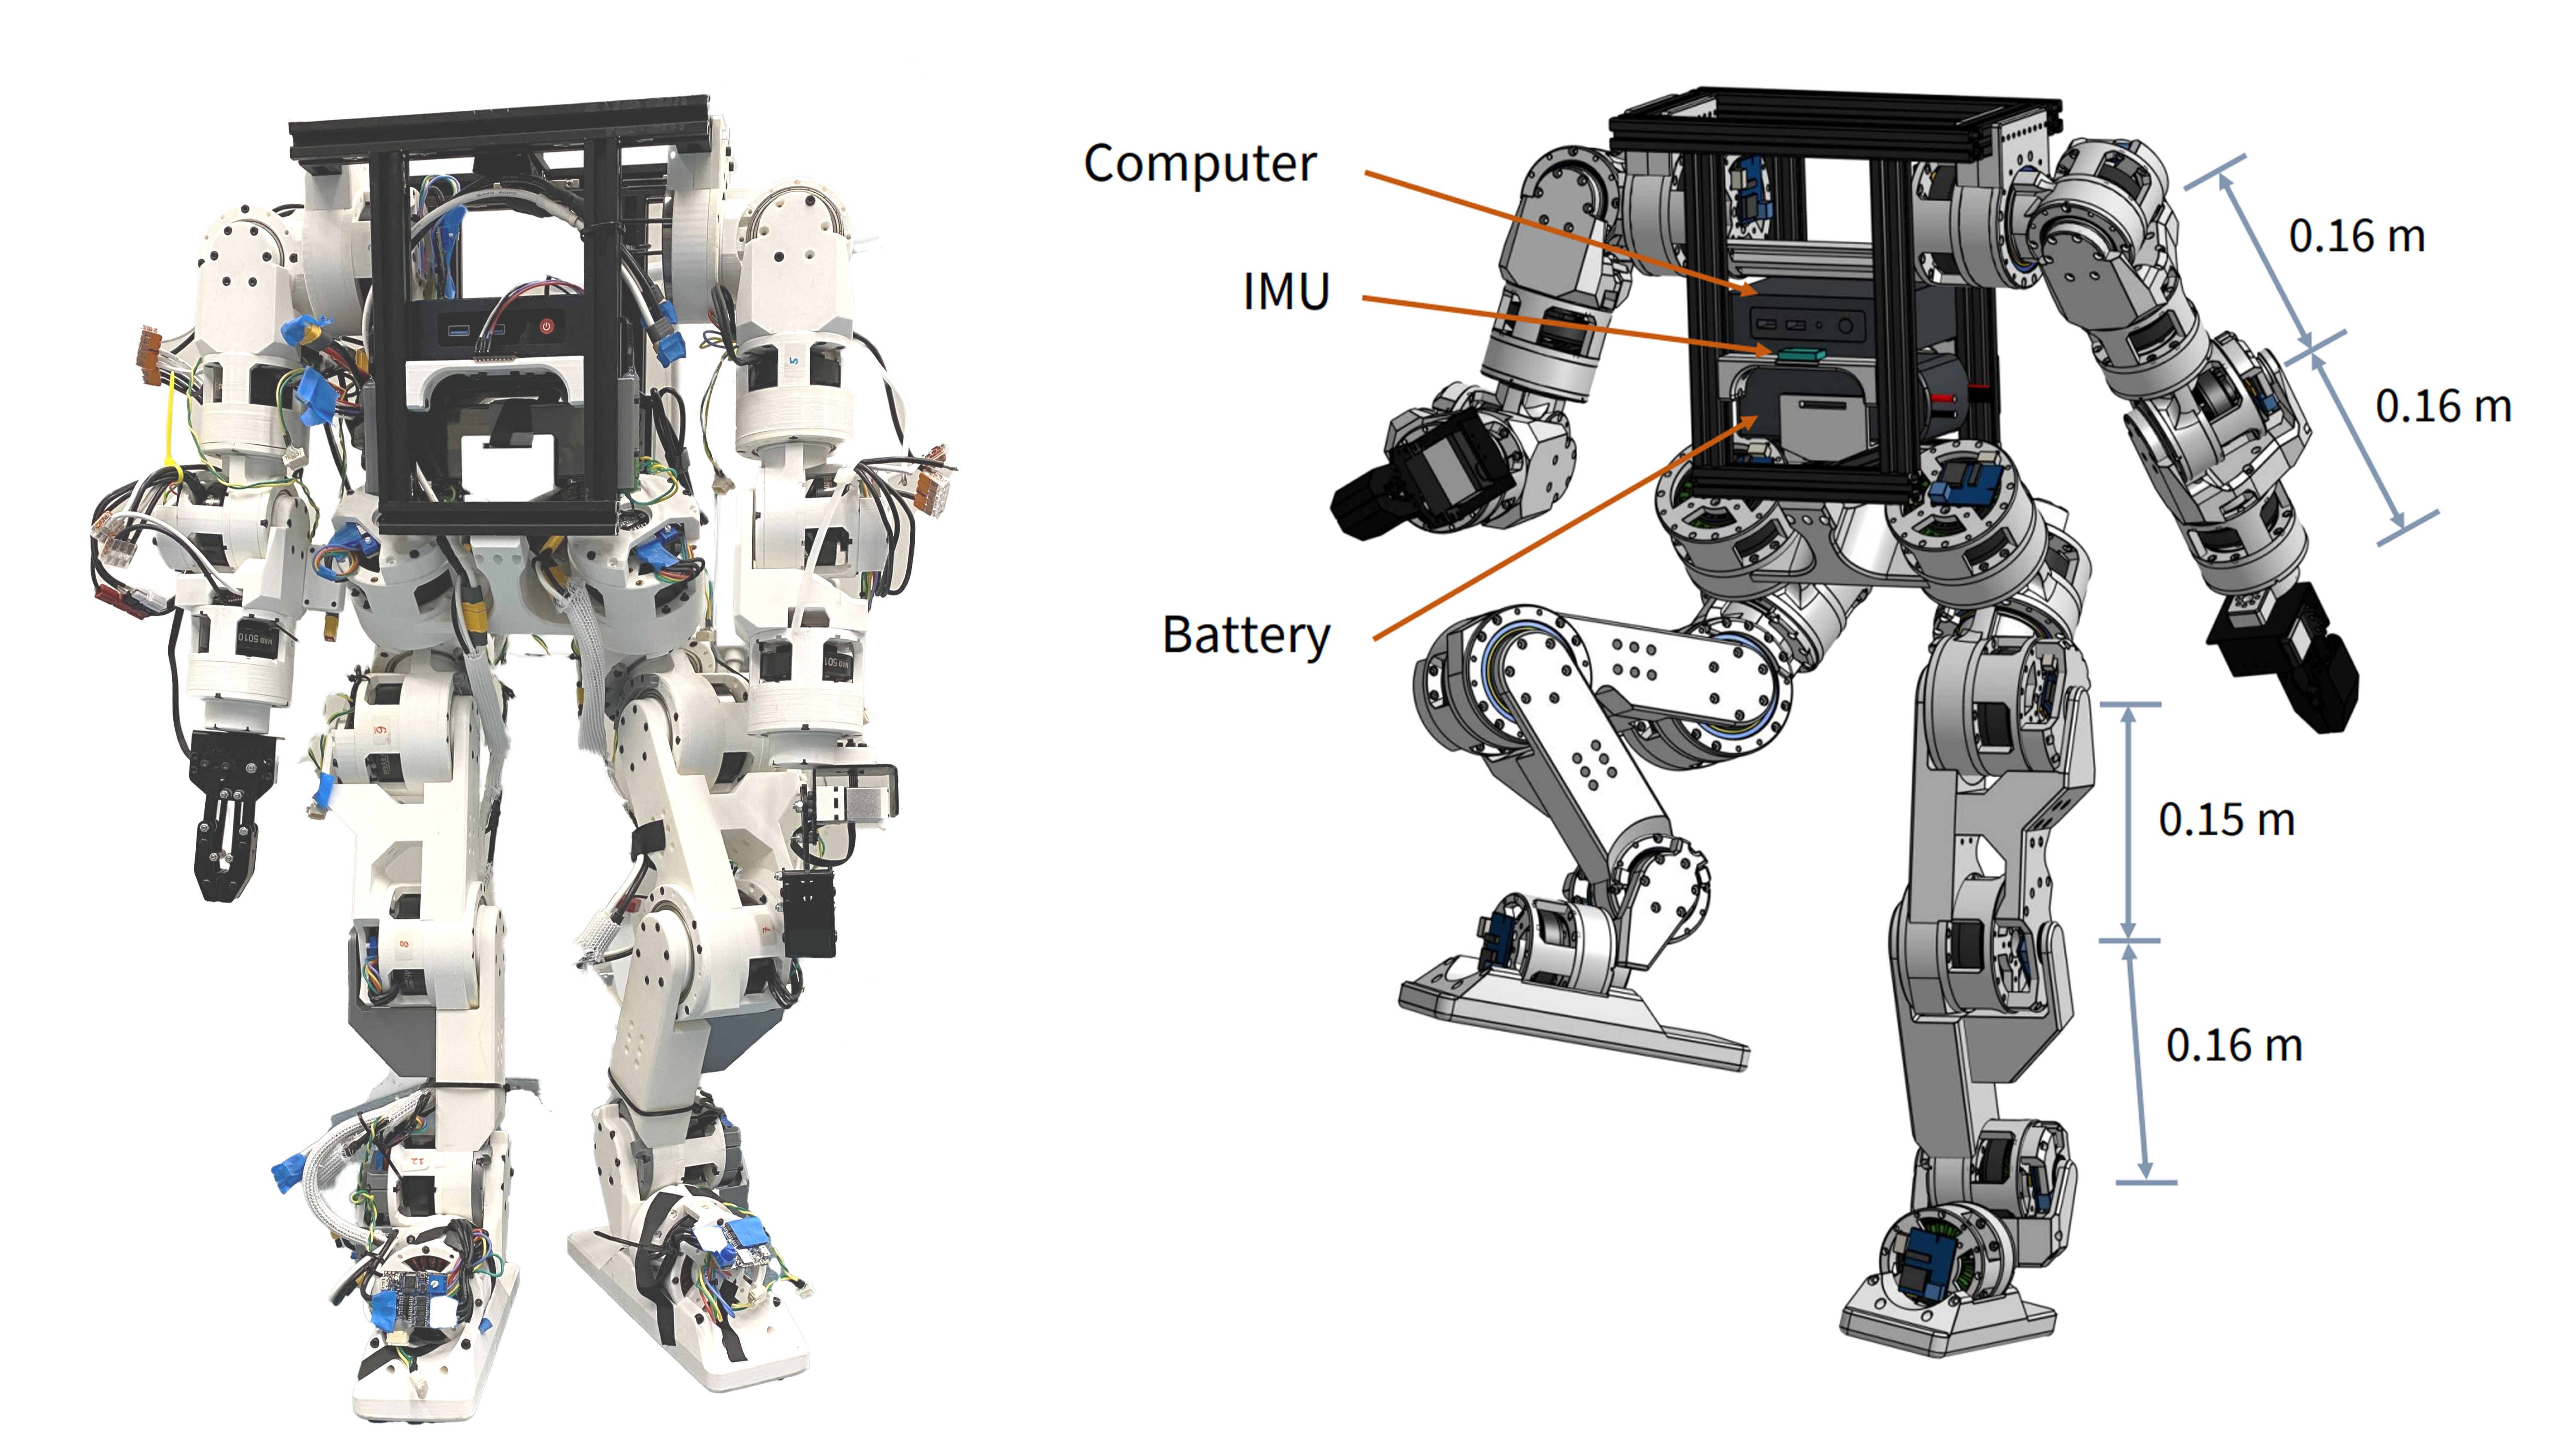
Berkeley Humanoid Lite: Affordable Open-Source Robot with DIY Actuators
Explore the Berkeley Humanoid Lite, a budget-friendly open-source robot featuring 3D-printed actuators under $5,000 USD. Learn how its modular design benefits DIY projects.
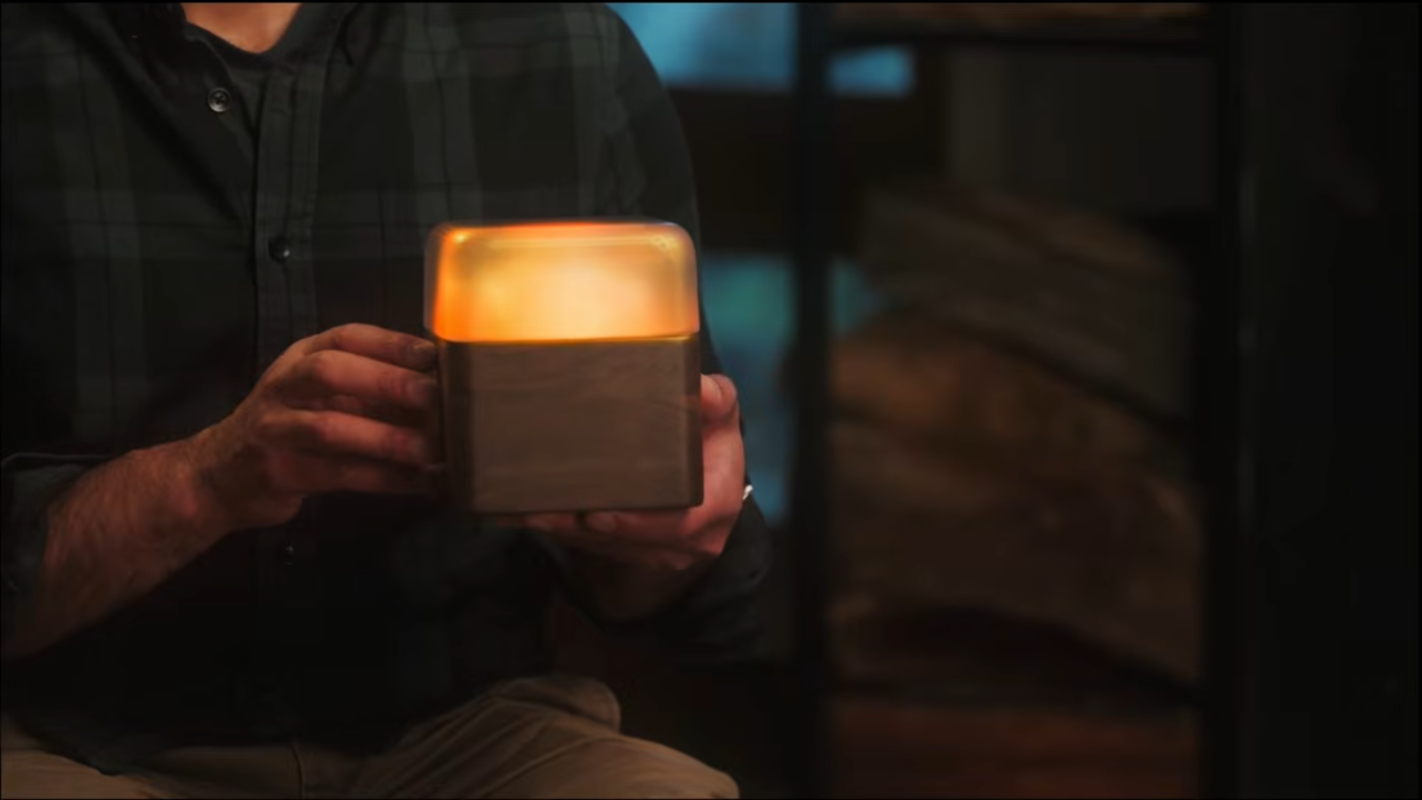
Woodstove Safety Monitor: Oru System Alerts Users to Temperature Fluctuations
Discover how the Oru woodstove assistant helps prevent dangerous chimney fires by monitoring exhaust gas temperatures and alerting users to temperature changes.
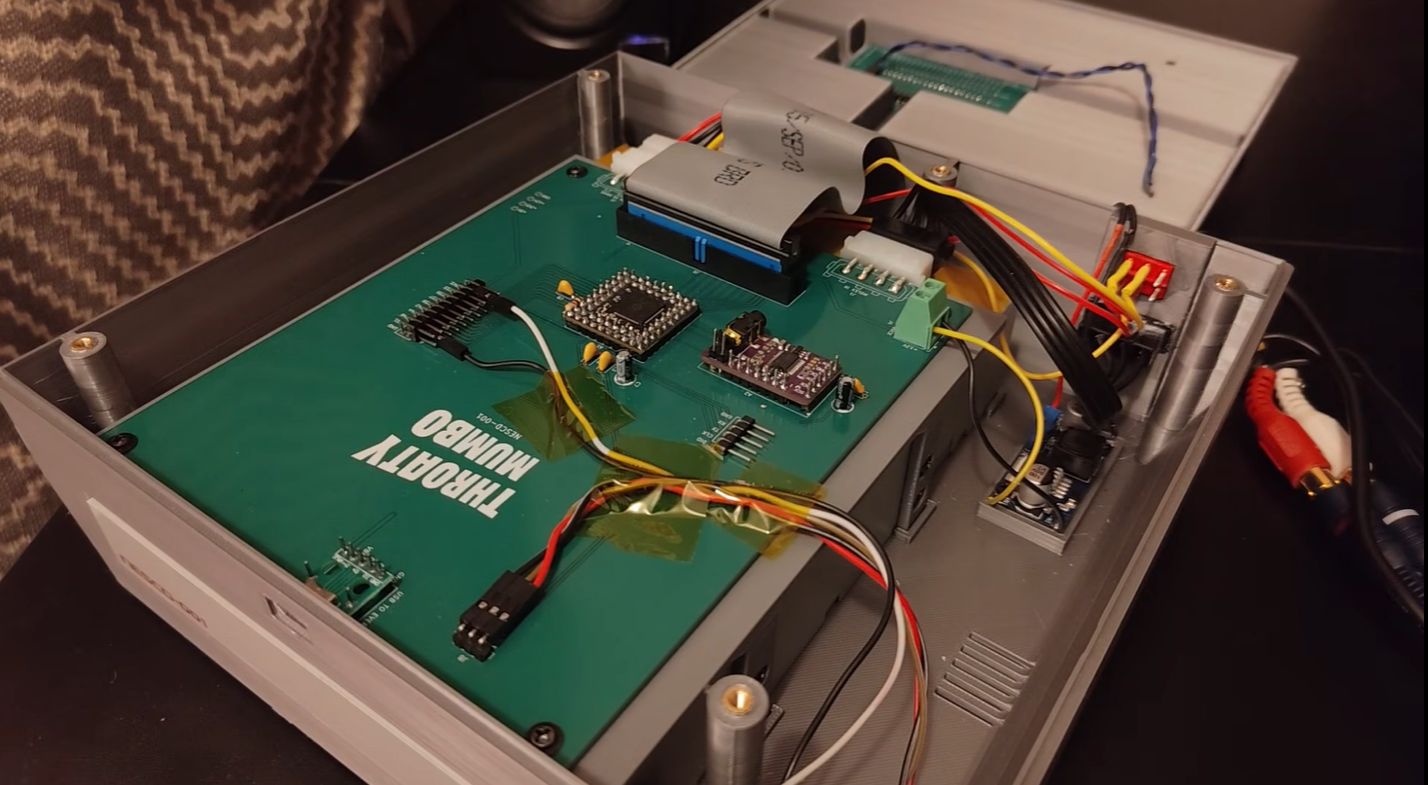
NES CD Add-On Revives 1980s Gaming with Optical Storage
Explore how a DIY project integrates a CD drive with the NES using an RP2350B microcontroller and Everdrive N8 Pro for expanded storage and audio playback.

Mumbai’s Vile Parle Cypher is giving unheard rappers a voice
Enrich and Ultimo impress

Karnataka CM Signals Review of 5% Park Land Amendment Bill in Assembly

